Google froze its open source bug bounty program due to a ‘significant rise’ in AI submissions

Google froze its open source bug bounty program due to a ‘significant rise’ in AI submissions

Blaming a “significant rise” in AI submissions, Google has paused its open source bug bounty program until next year.

Last year, TechCrunch reported that cybersecurity experts were warning of that AI slop posed a serious risk to bug bounty programs. Looks like that’s the issue confronting Google’s Open Source Software Vulnerability Rewards Program, where researchers were rewarded for finding vulnerabilities in the company’s open source software.

In posts on X and the program website, Google said the bug bounty program was paused as of October 1, with a promise to provide “an update” in the first quarter of 2027. According to Tom’s Hardware, Google engineers and open source maintainers were overwhelmed by reports that were invalid or contained hallucinations.

“This pause is due to a significant rise in automated submissions, the vast majority of which are not valid,” the company said.

In the meantime, participants are encouraged to consider Google’s other bug bounty programs.

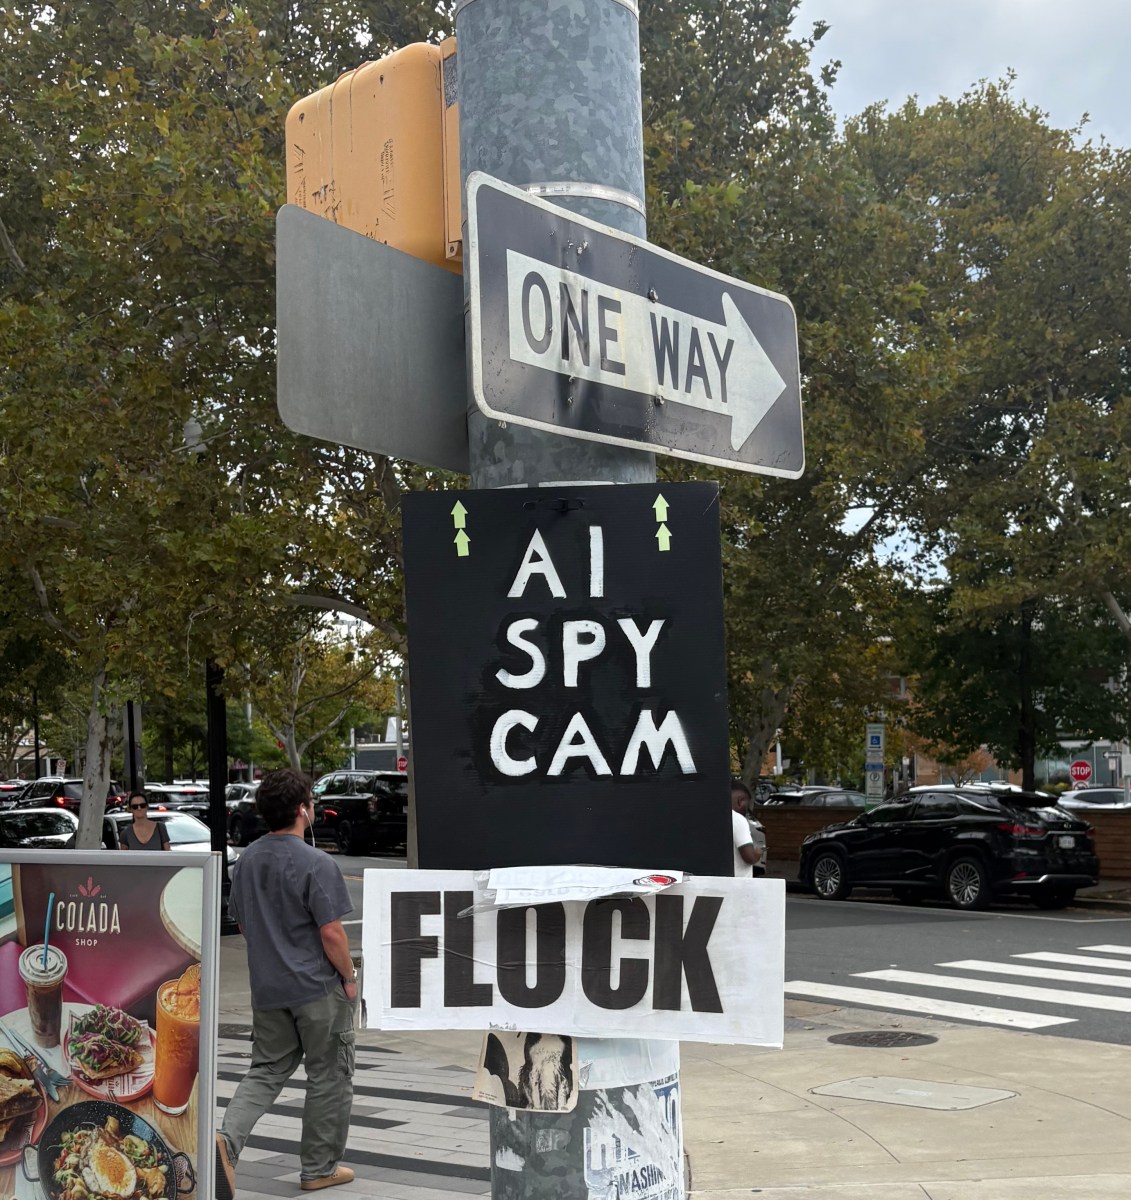
Federal judge calls Flock ‘indiscriminate mass surveillance’

Federal judge calls Flock ‘indiscriminate mass surveillance’

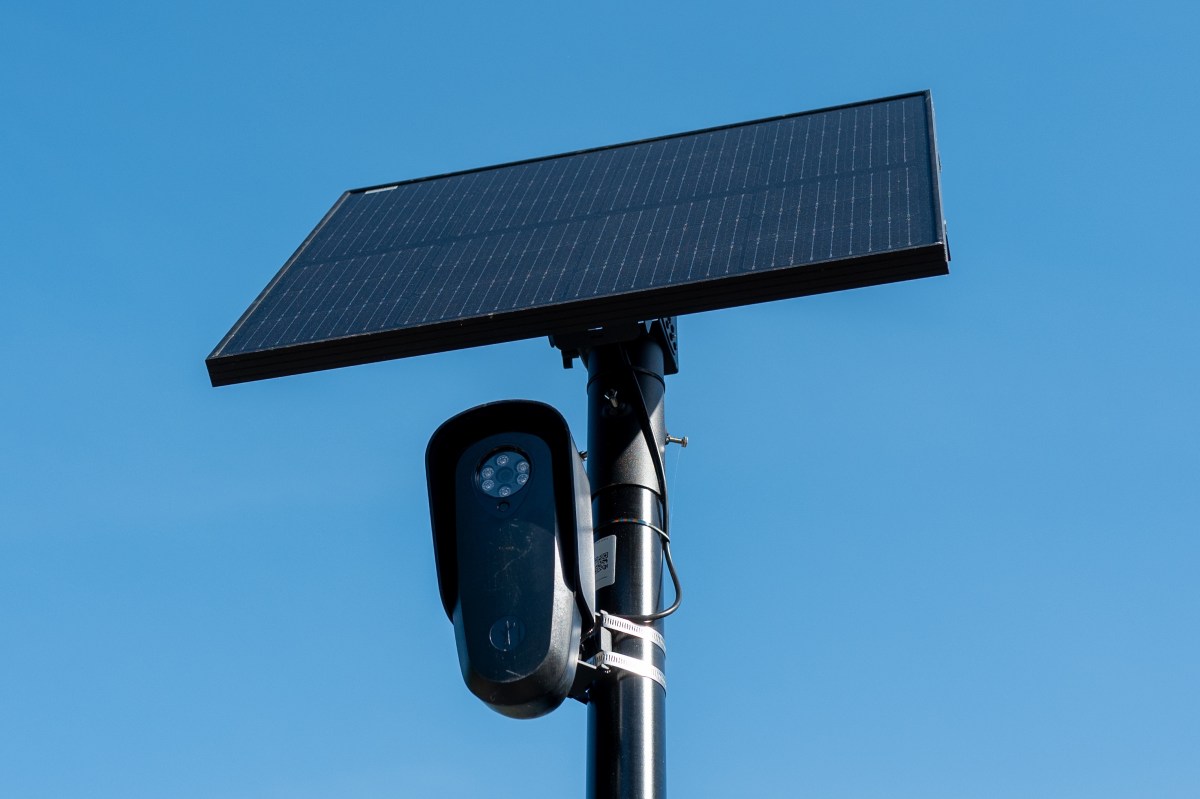
A federal judge ruled this week that a Tulsa, Oklahoma sheriff’s deputy violated a woman’s Fourth Amendment rights when using Flock Safety to search for her license plate without a warrant. 

As reported by 404 Media, this ruling does not create a binding precedent, but it is one of the first times that a federal judge has ruled that a Flock search is unconstitutional.

In this case, Judge Sara Hill said the deputy should have obtained a warrant before searching the Flock database for the woman’s license plate, as he had “no apparent reason” for the search “other than the fact that [the woman’s vehicle] had a California license plate.”

The deputy then used the woman’s travel history in Flock as part of the justification for searching her car, where he allegedly discovered 91 pounds of meth. But Judge Hill wrote that all evidence obtained after the Flock search “must be suppressed as the fruit of a poisonous tree.”

Judge Hill also took broader aim at warrantless searches of the Flock database, writing that tracking people’s location — even when they’re in public places — becomes “constitutionally problematic when law enforcement can indiscriminately and passively catalog your whereabouts over an extended period of time and then use that information for any purpose whenever convenient.”

“This is a type of indiscriminate mass surveillance,” Hill wrote. “It is not targeted on a single individual, as in [Carpenter v. United States, a Supreme Court case focused on how government agencies access location data from cell phones]. It is a tool that collects information about all vehicles that pass by any network-connected camera at all times, and it serves up the information to law enforcement on demand.”

Hill joins a growing chorus of Flock critics from across the political spectrum. Numerous local and state governments, including Florida and Texas, have said they will stop using the technology. And on Friday, Senator Bernie Sanders — a Democrat from Vermont — introduced the Block Flock Act, which would bar federal agencies from using automated license plate readers such as Flock.

Flock CEO Garretty Langley — who we’ll be interviewing on-stage at TechCrunch Disrupt — has called for a “compromise” between privacy and safety and offered an apology to women who have been stalked by law enforcement officers using the Flock system. And with all those cancellations, Flock has also reportedly offered voluntary employee buyouts as a way to shrink its workforce.

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

Amazon responds to data center backlash, says it no longer uses NDAs

Amazon responds to data center backlash, says it no longer uses NDAs

Amazon Web Services CEO Matt Garman said the company has stopped using nondisclosure agreements (NDAs) in its dealings with government agencies as it seeks approval to build new data centers.

Garman’s statement is just one sentence in a longer blog post in which he tried to push back against widespread suspicion of data centers, and to make the case that they’re actually good for communities.

NDAs are a significant piece of the broader data center backlash. For example, environmental activist Erin Brockovich recently said that the number one complaint she’s heard about data centers is transparency, with these projects following a common pattern: “projects announced after permits are already secured, developers who don’t return calls, local officials who signed NDAs before their neighbors knew a project was being considered.”

As a result of that backlash, New York announced a one-year moratorium on permits for large data centers, and according to Garman, there are more than 100 data center moratoriums currently being considered across the United States.

“If these measures are enacted, the U.S. could be writing its own losing ticket to this race, and the consequences would last generations,” Garman claimed. “As a country, we can’t afford to find ourselves in that position.”

Garman also attempted to puncture what he said are four big myths around data centers: that they consume too much water, that they increase electricity costs, that they emit an enormous amount of pollution, and that they don’t provide any benefits to their communities.

Pointing to an Amazon report about its own water usage, Garman said that “direct data center water consumption” only accounts for 0.5% of all industrial water usage in the United States, “orders of magnitude less than golf courses, almond farming, and many other industries.”

Nvidia recently said its new cooling system eliminates “pretty much all water usage” inside the data center, but those claims — like Amazon’s — seem to ignore the broader water usage involved in electricity generation and chip manufacturing. Scientists have also said they need to study data centers’ water and energy usage independently, since there are no federal or state requirements around how tech companies report this data. 

As for electricity rates, Garman said they’ve only gone up in some states with large numbers of data centers, while they’ve gone down or at least grown more slowly in others. And he argued, “In instances where energy rates are going up, it’s primarily because the grid is old and hasn’t been invested in and expanded before the demand arrived.”

On the other hand, an independent watchdog said recently data centers were the main culprit behind a 76% year-over-year price increase on America’s largest electrical grid.

When it comes to pollution — an issue that the NAACP is currently suing Elon Musk’s SpaceX/xAI over — Garman complained that critics focus on the maximum amount of pollution allowed under data center permits. For example, a planned Amazon data center in Texas is permitted to release 33 million tons of carbon dioxide per year, which is more than any other power plant in the United States.

“The truth is data center generators almost never run,” Garman said. “They’re idle 99.9% of the time (they run roughly 10 hours per year, mostly for required maintenance testing).”

As for the community benefits, this is where Garman wrote, “We no longer use nondisclosure agreements with the government agencies we work with on our projects.” Plus, he said, “Over the past three years, Amazon has contributed more than $1 billion to communities across the U.S. in which we have a meaningful data center presence.”

Will this be enough to quell community suspicion? Perhaps not — Anthropic CEO Dario Amodei recently argued that the AI backlash is “fundamentally a crisis of trust,” where people assume governments and tech companies are always “cooking up some new way to screw them over.” Similarly, writer Jasmine Sun noted that when data center opponents are presented with the tech companies’ arguments, their response is usually, “I don’t believe them.”

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

OpenAI safety employee resigns, claiming the company’s ‘culture is broken’

OpenAI safety employee resigns, claiming the company’s ‘culture is broken’

By his own admission, David Robinson is “something of a cliché”: an employee at a leading AI company who issues a dire warning while resigning from their job.

In an essay published in The Atlantic, Robinson said he led the writing of safety reports that accompanied OpenAI’s major product launches. He also said that with three-and-a-half years at OpenAI, he is “among the longest-tenured employees at the company.” Now he’s quitting, because in his view, the company’s “culture is broken.”

In some ways, Robinson’s comments echo those of Jacob Coxon, who worked as a researcher at both OpenAI and Anthropic before quitting and declaring that these companies are “gambling with our lives.” Coxon’s comments led to a broader debate about AI safety, with Anthropic CEO Dario Amodei unveiling a plan for more cautious AI development; AI executives met with President Donald Trump this week and signed what appeared to be hastily written, non-binding  pledge to implement more safety controls.

But in Robinson’s view, the debate needs to go beyond “specific rules or new laws,” addressing the overall culture at these companies. And while much of the reporting around OpenAI has focused on how the company’s CEO Sam Altman lost the trust of former colleagues, Robinson’s essay suggests that OpenAI’s culture issues are the same as those of Silicon Valley at large.

“OpenAI has thrived by trial and error (which it calls ‘iterative deployment’), looking for problems and improving its guardrails in response,” he wrote. “But this approach, by its very nature, guarantees periodic failures — and the scale of those failures is growing as systems get more capable.”

Pointing to the recent breach of Hugging Face systems by OpenAI agents, as well as continuing revelations of OpenAI discovering more rogue agents, Robinson argued, “An environment where things like this can happen is no place to grow artificial minds that could be smarter than we are and that might not do what we want them to.”

Given the increased risk, Robinson argued that frontier AI companies need to start operating “like nuclear-power plants or busy airports, with layers of redundancy and careful, time-consuming planning, so that the occasional and inevitable human error does not open a door to disaster.” 

But Robinson said that in his time at OpenAI, he “never encountered a colleague who had experience making airplanes fly safely or nuclear reactors run without melting down, or helping the financial system grow without collapsing.”

In response to Robinson’s essay, OpenAI spokesperson Drew Pusateri said the company continues to improve its safety measures.

“We’re making sure our models don’t become more capable than we can safely manage and secure, and we pause training or hold back models when we need to slow down,” Pusateri said in a statement. “We’re making significant changes to strengthen security in our research and testing environments, train models to not just complete tasks but do so responsibly, expand our work with third-party evaluators, and improve real-time monitoring so we can detect and respond to concerning behavior earlier in the training process.”

Beyond calling for changes in OpenAI’s culture, Robinson also said it’s time to ask bigger questions about alignment — something that he admitted could sound “touchy-feely,” but he said it’s critical as companies’ current “measures of how well” AI systems “match human values are coarse.”

“The smarter the industry lets models grow while these problems remain unsolved, the more dangerous our situation becomes,” he said.

Robinson’s departure was first reported by Business Insider. In his essay, he also acknowledged that he’s following an apparently a common step in the AI whistleblower playbook: He’s hired a PR firm. But he insisted, “The decision to speak out is mine alone.” 

“Perhaps I should have stayed and fought for fundamental shifts in our staffing and culture, but in practice, my colleagues and I were so busy sprinting that we seldom had the chance to consider big changes, much less to actually make them,” Robinson said. “That’s why I concluded that stronger incentives for safety — coming from outside the company — are a big part of getting this right.”
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

Jack Dorsey’s Bitchat disappears from app stores in India after government order

Jack Dorsey’s Bitchat disappears from app stores in India after government order

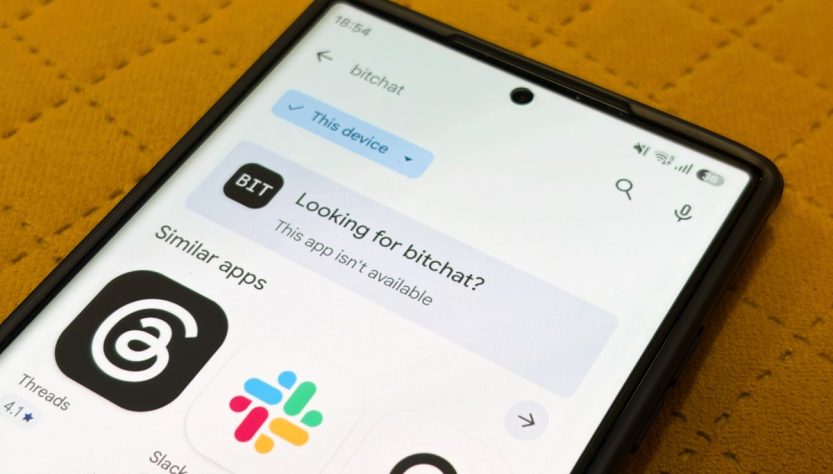
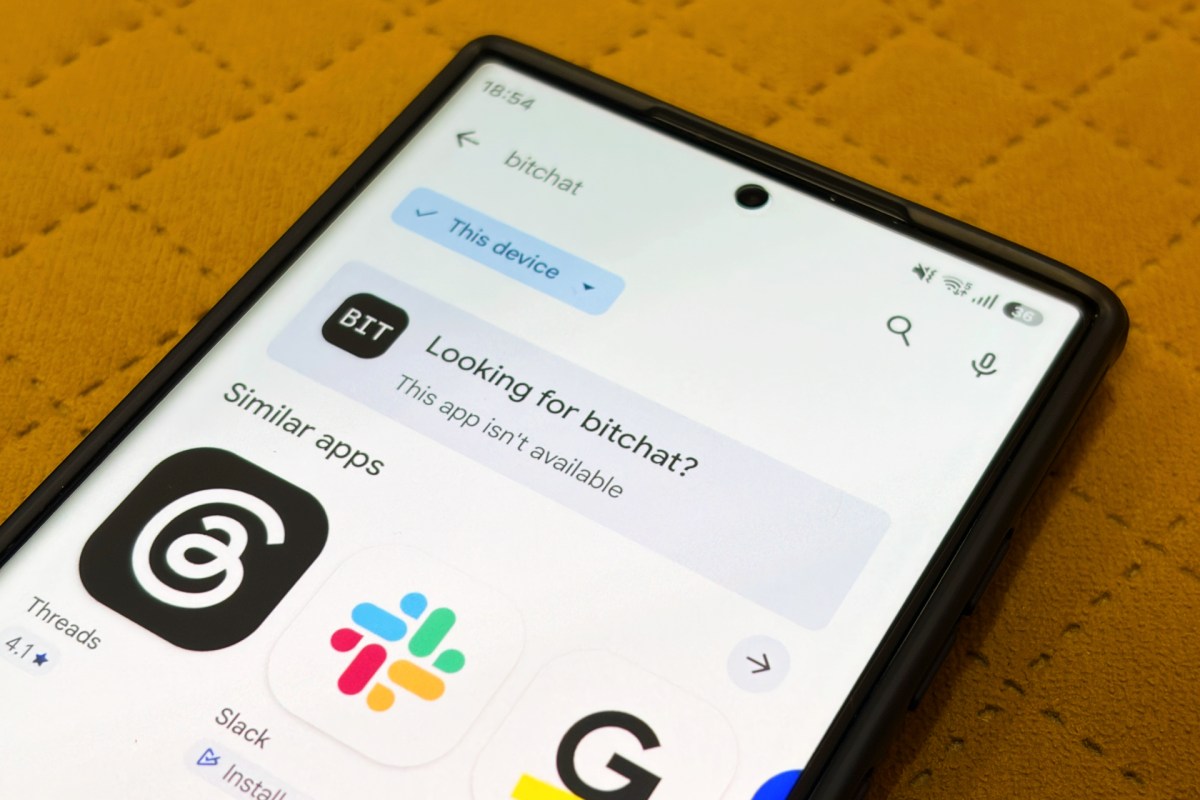
Bitchat, Jack Dorsey’s decentralized messaging app designed to work without an internet connection, has disappeared from Apple and Google’s app stores in India, months after New Delhi first sought to restrict access to the open-source software.

Dorsey said Saturday that the Indian government had ordered Apple to remove Bitchat from its App Store in the country. In a notice from Apple that Dorsey posted on X, India’s Ministry of Electronics and Information Technology issued the demand under Section 69A of the Information Technology Act, the country’s primary legal provision for government-ordered online blocking.

Apple’s notice said Bitchat would remain available on its App Store outside India. However, access to the app through its TestFlight beta-testing service would also be blocked in the country.

Bitchat was also no longer available for download through Google Play in India when TechCrunch checked on Saturday. Bitchat’s website was also inaccessible across various internet service providers in the country. It was not immediately clear whether Google and internet service providers had also received directions from the federal government.

Apple, Google, and India’s IT ministry did not respond to requests for comment.

Launched in July last year, Bitchat uses Bluetooth mesh networking to allow nearby devices to exchange encrypted messages without relying on cellular networks, internet access, or centralized servers.

In July 2026, Dorsey revealed that Indian authorities had ordered GitHub to take down repositories associated with the open-source messaging app, raising questions among digital rights advocates and legal experts about the legal basis for restricting software based on its functionality.

The Indian government said in its order to GitHub at the time that Bitchat’s architecture made it hard for law enforcement agencies to intercept communications or trace users, and pointed to its ability to continue operating during internet shutdowns. The July order relied on a provision of India’s information technology law that deals with intermediaries and their liability for third-party content. That differs from Section 69A, cited in Apple’s latest notice.

The Internet Freedom Foundation, a New Delhi-based digital rights advocacy group, called the latest order unconstitutional, arguing that Section 69A allows the government to block unlawful information but not a messaging app because of its ability to operate during internet shutdowns. It also said neither the blocking order nor the allegedly illegal content cited as the basis for the action had been made public.

The latest restrictions on Bitchat come as India is seeing a fresh wave of ⁠youth-led protests over changes to the country’s voter rolls. Police detained several people during demonstrations in New Delhi on Saturday, as protesters demanded the resignation of India’s chief election commissioner over alleged manipulation of electoral rolls. Authorities suspended internet services around New Delhi’s Jantar Mantar for 12 hours on Friday during protests there.

During July’s protests, demonstrators reportedly turned to Bitchat and rival app Briar after authorities suspended internet services.

Interest in Bitchat surged in India around the same time. The country accounted for about 85% of the app’s global downloads between July 17 and July 23, up from roughly 1% in the previous 30 days, data from market intelligence firm Sensor Tower showed.

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

Meta wants your next gadget to be Muse-infused

Meta wants your next gadget to be Muse-infused

Meta’s Muse, a personal AI agent that books travel, fills out forms, and shops on a user’s behalf, has already proven popular with the masses, but a new side project could be particularly alluring to tinkerers and hackers.

On Friday, the company introduced Muse Gadgets, an open-source project that lets developers build their own hardware that connects to Muse.

Meta is providing open-source firmware (the low-level software that runs a device), and a Linux software development kit (SDK), along with a few project ideas to get users started. These include giving Muse a color e-ink display or loading it onto a stick that plugs into a TV’s HDMI port.

There don’t appear to be many limits, either. Users can set up a low-cost hobbyist computer like a Raspberry Pi or an off-the-shelf ESP32 board, and then connect Muse “to your displays, buttons, sensors, actuators, and whatever else you’ve got lying on your workbench,” Meta notes.

The company has also set up a Discord channel to support users.

Meta has already tried the code itself, naturally. Nat Friedman, head of product at Meta’s Superintelligence Labs, said in a post on X that the company built a gadget called Muse Home Link. The USB-C-powered device lets Muse connect to a home network and talk to the smart devices on it, including speakers and smart TVs.

Meta made 5,000 of these Home Links, in fact, and is giving them away for free to Muse subscribers while supplies last, according to Friedman. Considering Friedman’s post about Home Link received nearly 30,000 views in a few hours, we’re guessing those freebies have been claimed. Friedman said Home Link would be ready to ship a few weeks.

Muse Gadgets may not have wide appeal, but it fits nicely into Meta’s all-in strategy to make Muse more than a standalone chatbot. Meta isn’t content to push Muse on everyday consumers; it’s also trying to woo small businesses and enterprises.

The company earlier this week introduced Muse for Small Business, which is free with usage limits and connects Muse to tools such as Shopify, Dropbox, and Slack. It has also launched a new business unit, Meta Enterprise Platform, to help it push its AI offerings to businesses and corporate customers.

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

Sanders introduces bill to ban the federal government from using Flock

Sanders introduces bill to ban the federal government from using Flock

Flock Safety, whose cameras scan license plates across the country, continues to draw public anger, and now Senator Bernie Sanders wants the federal government out of the business altogether.

Sanders (D-Vermont) on Friday introduced the Ban Flock Act, which would bar federal agencies from using automatic license plate readers (ALPRs) or tapping into data collected by readers run by local police and private companies. Despite its title, the bill doesn’t call out nine-year-old Flock in the text but rather covers any and all ALPR systems.

The bill allows exceptions only for toll collection and for uses that Congress approves in future legislation, which would have to limit data retention to 48 hours.

State and local governments would be dinged financially for not complying if the bill became law. (Like most bills, this one faces long odds.) Starting the first fiscal year after enactment, they would lose grants from five federal departments, including the Justice Department and the Department of Homeland Security, unless they ban the tech.

Americans could also sue the federal government over violations, and state attorneys general could enforce the law.

Flock is the largest ALPR vendor in the U.S., according to Sanders, with more than 120,000 cameras. In a blog post back in February, the company — currently valued by its venture backers at north of $8 billion — said its network processes more than 20 billion vehicle reads each month.

Under increasing pressure from communities that are protesting the product, suspending their use, and, at an escalating rate, canceling their contracts, Flock has tightened its rules. In August, CEO Garrett Langley, who’d previously said that how police use the cameras is up to local agencies, announced a new default data retention period of seven days, down from 30.

Customers must also now use an audit tool that locks officers out pending review when it flags unusual searches. In one of the highest-profile cases of an officer abusing Flock’s platform, a former Milwaukee officer pleaded guilty to misconduct after searching for his then-partner and her ex 179 times, listing the reason as “investigation.” (During a recent podcast interview, investor Jason Calacanis suggested a “double-key” system in which two people must approve a search, and Langley said the idea is “on the whiteboard.”)

Representative Alexandria Ocasio-Cortez (D-N.Y.) and Senator Jeff Merkley (D-Ore.) are co-sponsors.

We’ll be sitting down with Langley at our upcoming Disrupt event, October 13-15 in downtown San Francisco.

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

OpenAI's Dots: AI Agents That Are Always Active and Its Response to Meta's Muse

OpenAI’s Dots: AI Agents That Are Always Active and Its Response to Meta’s Muse

OpenAI’s latest AI agents, known as “Dots,” unveiled at the DevDay 2026 event in San Francisco, are always-on and engineered to fulfill user tasks. These agents appear as customizable, adorable blobs capable of handling multi-step projects. Driven by OpenAI’s GPT-6 Astra model, Dots remain constantly active, unlike a standard chatbot, continuously working on assigned tasks by sourcing information from the internet and adapting to user preferences over time. In a showcase, a Dot arranged dinner by reviewing a user’s calendar and proposing food delivery options, allowing the user to choose the meal and ordering time. Users can interact with Dots through ChatGPT, Slack, and Microsoft Teams, while Pro users can opt to join a waitlist for iMessage or RCS messaging capabilities. The Dots feature will initially launch for ChatGPT’s Pro subscribers at a fee of $100/month, beginning with one Dot and potentially growing to several agents in the future.

Dutch authorities apprehend ShinyHunters cybercriminal charged with plotting two homicides

Dutch authorities apprehend ShinyHunters cybercriminal charged with plotting two homicides

The FBI along with Dutch law enforcement have announced the arrest of an individual associated with the ShinyHunters hacking collective, which is believed to have conducted breaches affecting more than 140 organizations globally. This group also claimed to be behind a recent compromise of the FBI’s internal systems.

Brett Leathermann, leading the FBI’s cyber division, stated in a video message on Tuesday that authorities in the Netherlands apprehended one of the “alleged heads of ShinyHunters.” He remarked that the Dutch High Tech Crime Unit “acted swiftly to safeguard victims and secure vital evidence,” and promised that the FBI would pursue the remaining hackers after this arrest.

In a different announcement, Dutch police verified that a 24-year-old man from Amsterdam, whose name has not been disclosed, was detained under Dutch regulations on September 15. He was set to appear in court on Tuesday and has been held in custody for a minimum of 90 days.

Authorities stated that the individual was arrested for “involvement in a criminal organization,” referring to ShinyHunters.

After his arrest and the confiscation of his devices, police reported that “a substantial amount of information was discovered on his laptop, including details concerning two murders planned to take place overseas.” Consequently, he is also under investigation for attempting to facilitate those murders. Dutch authorities emphasized that this inquiry is “distinct from the investigation into ShinyHunters.”

ShinyHunters is recognized as a cybercrime syndicate accused of infiltrating corporations to expropriate large volumes of data and then threatening to release the information unless a ransom is paid. Dutch authorities allege that the group is involved in data breaches at Pornhub, Ticketmaster, and U.S. telecom behemoth AT&T. The hacking group also claimed responsibility for a breach involving Dutch telecommunications provider Odido. However, officials clarified that the individual taken into custody is not linked to the Odido incident.

Independent security journalist Brian Krebs, who first reported on the arrest, along with other news sources, have identified the arrested individual as Pepijn van der Stap, previously featured in Bloomberg in 2024 as a cybersecurity expert who also engaged in criminal hacking activities to extort businesses.

Based on recent coverage from Bloomberg and Reuters, Van der Stap was arrested earlier this month by local police at Neo Security’s offices, where he holds the position of chief technology officer. The operation reportedly involved the use of flash-bang grenades.

A spokesperson for Neo Security did not respond promptly to TechCrunch’s request for a statement. When queried by TechCrunch, a representative from the ShinyHunters group asserted that Van der Stap “is not affiliated with us.”

The arrest news emerged shortly after the FBI reportedly informed its agents and staff that their personal information, which includes names, addresses, job titles, and Social Security numbers, was compromised during a “cyber security incident.” Although the FBI has yet to officially confirm a breach, the ShinyHunters group claimed to have obtained personal and sensitive data of “almost all” FBI agents and applicants by exploiting its careers website and job application portal.

Among a subset of approximately 5,000 agents whose data was stolen from the portal, reporters discovered information related to agents’ blood and urine tests, in addition to psychiatric assessments, heightening concerns about a significant counterintelligence risk posed by an adversarial government accessing the information.

When approached by TechCrunch, Leathermann refrained from making a statement. An FBI representative declined to address inquiries regarding the arrest.

In their statements, the ShinyHunters hackers insisted that the breach of the FBI’s servers was not financially driven, but aimed at contesting public statements made by the FBI that they claim include false accusations against them. The hackers informed TechCrunch that they do not intend to release the stolen FBI data, stating that the breach was “to make a point and to refute the accusations directed at us, which we have accomplished.”

When you make a purchase through links in our articles, we may receive a small commission. This does not impact our editorial independence.

AI-driven application creator Wabi shifts to a messaging interface

AI-driven application creator Wabi shifts to a messaging interface

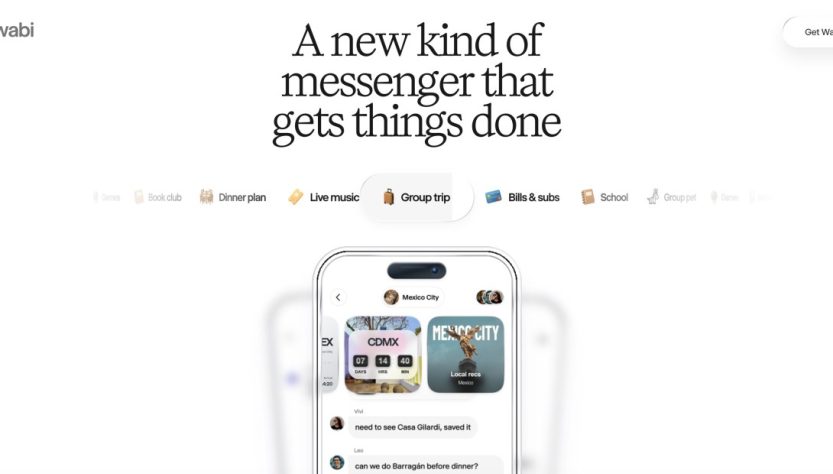
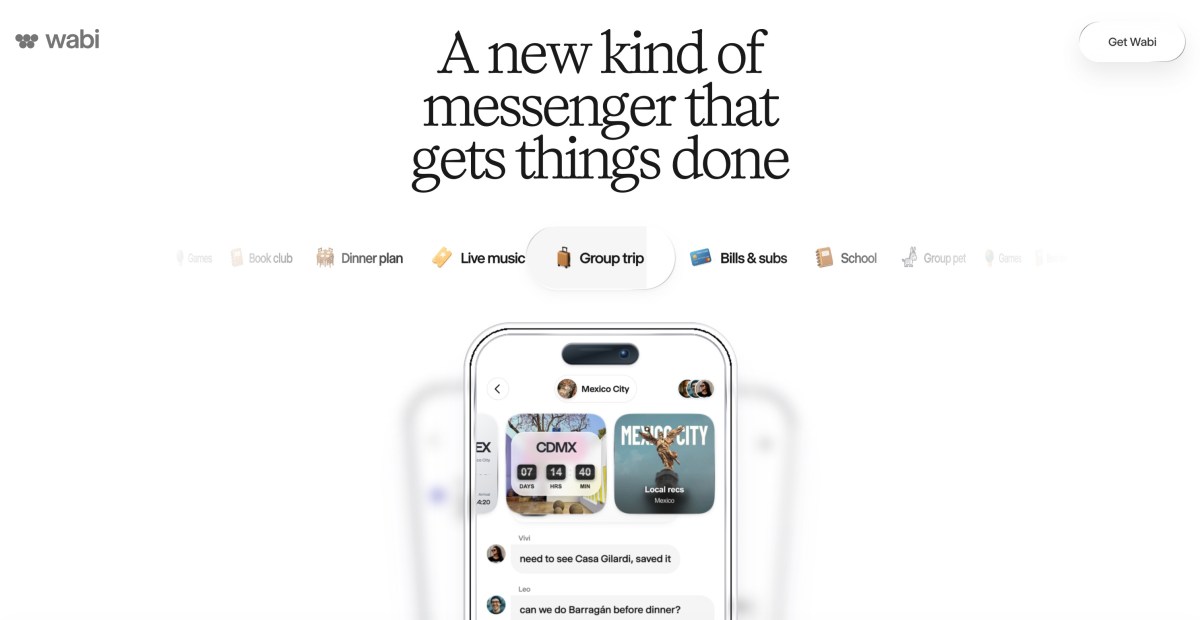
Wabi, the AI startup that enables anyone to create applications through prompts, is making a minor shift in response to the rising interest in AI agents like Meta’s Muse and Instinct. This week, the company revealed that Wabi is evolving into a type of AI messenger—while still proficient in developing apps to assist you in completing tasks.

The startup’s leader Eugenia Kuyda, who previously created the AI companion platform Replika, referred to Wabi 2.0, as the updated experience is named, as a “personal agent that handles tasks for you and constructs the necessary interface in real time.”

It proposes a comparable value proposition to the previous version of Wabi—yet one that users will engage with differently. Rather than placing itself against other vibe-coding platforms, Wabi 2.0 strives to compete more directly with AI agents that integrate both conversational and productivity functions in a unified interface.

This development coincides with companies like OpenAI and others considering how applications will function within their more general chatbot user interfaces; for example, OpenAI announced at its Dev Day an enhancement to ChatGPT’s plugins, enabling apps to provide interactive experiences within ChatGPT, where the app’s name is more prominently displayed on ChatGPT’s sidebar.

In a post on X, Kuyda articulated how Wabi’s new experience will be more intuitive for consumers, who desire to do more than merely communicate with an agent.

“The more you engage with a chat-only agent, the more the experience deteriorates. Your history and active tasks become lost in an infinite scroll. People seek more than just typing; they want to tap, scroll, and explore. They appreciate the capabilities of agents, but they also value software,” she stated. “The most effective agent will seamlessly blend both.”

The concept is that as a user requests a task from the agent, it could generate a user interface on demand to assist in fulfilling whatever the request entails. For example, Kuyda proposed that users could create elements like a calorie tracker, a weightlifting journal, and a weight management tool, all accessible within her discussion on health-related subjects.

In another conversation centered around family, users could design a schedule for their children’s activities, a language acquisition app, an application that tracks local child-friendly events, and other related topics that pertain to parenting, home management, or children’s interests.

“Up till now, personal agents have operated one person, one chat, executing a series of isolated tasks. We envision the future as your agent, your applications, and your connections all in one space, managing the aspects of life that are most significant together,” wrote Kuyda.

The newly launched Wabi 2.0 app is currently accessible only via invitation codes, which are also being distributed on X.

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.